Pytania i odpowiedzi (3 / 5)
Windows Serwer 2012 R2 70-411
101.
You have a server named Server 1.
You enable BitLocker Drive Encryption (BitLocker) on Server 1.
You need to change the password for the Trusted Platform Module (TPM) chip.
What should you run on Server1 ?
102.
103.
104.
105.
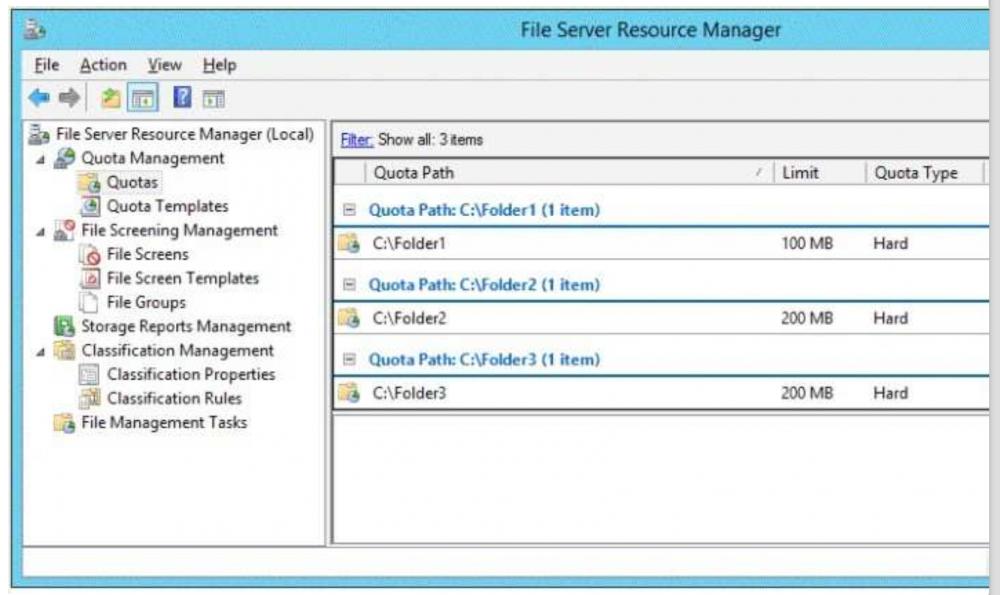
You have a server named Server1 that runs Windows Server 2012 R2. Server1 has the File Server Resource Manager role service installed.
Server1 has a folder named Folder1 that is used by the human resources department. You need to ensure
that an email notification is sent immediately to the human resources manager when a user copies an audio
file or a video file to Folder1.
What should you configure on Server1 ?
a file screen
106.
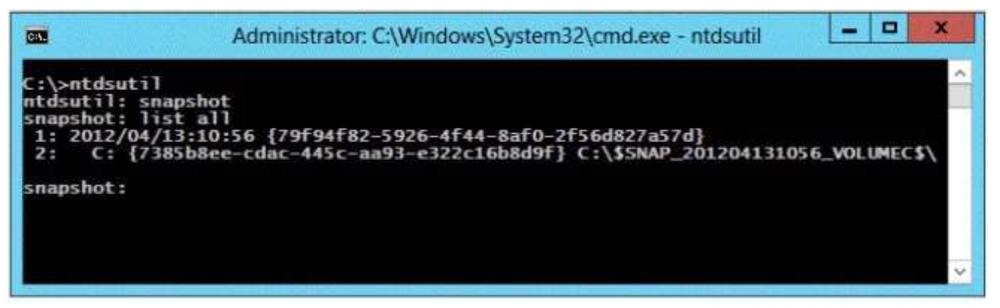
From a command prompt, run dsamain.exe -dbpath c:\ $snap_201204131056_volumec$\windows\ntds\ntds. dit -Idapport 33389
107.
Your network contains an Active Directory domain named contoso.com. The domain contains a read-only
domain controller (RODC) named R0DC1.
You create a global group named RODC_Admins.
You need to provide the members of RODC_Admins with the ability to manage the hardware and the
software on R0DC1. The solution must not provide RODC_Admins with the ability to manage Active
Directory objects.
What should you do?
From a command prompt, run the dsmgmt local roles command
108.
Your network contains an Active Directory domain named contoso.com. The domain contains a virtual
machine named Server1 that runs Windows Server 2012 R2.
Server1 has a dynamically expanding virtual hard disk that is mounted to drive E.
You need to ensure that you can enable BitLocker Drive Encryption (BitLocker) on drive E.
Which command should you run?
manage-bde -on e:
109.
the Security settings ot C:\Share1
110.
You have a failover cluster that contains five nodes. All ot the nodes run Windows Server 2012 R2. All of
the nodes have BitLocker Drive Encryption (BitLocker) enabled.
You enable BitLocker on a Cluster Shared Volume (CSV).
You need to ensure that all ot the cluster nodes can access the CSV
Which cmdlet should you run next?
Add-BitLockerKeyProtector
111.
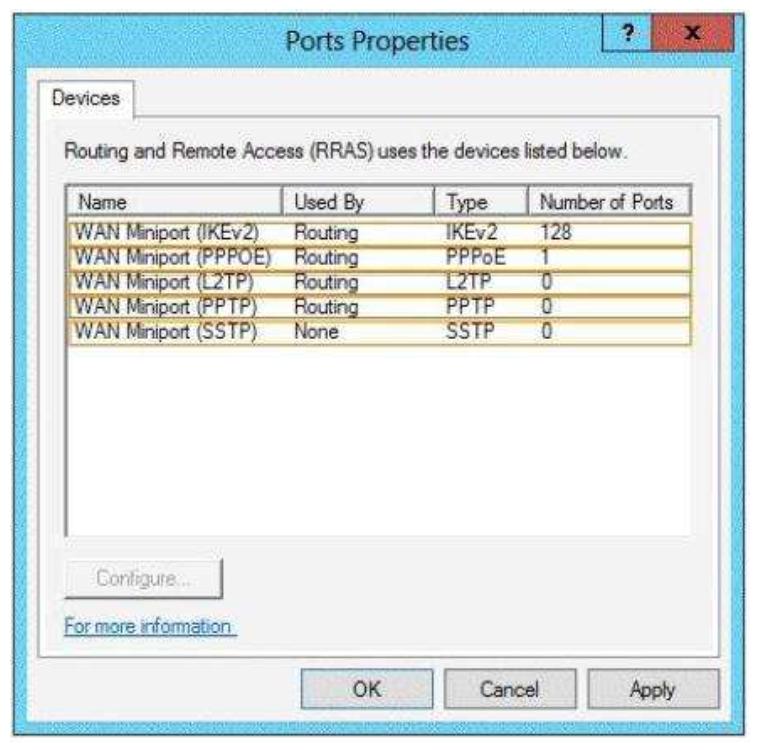
WAN Miniport (SSTP)
112.
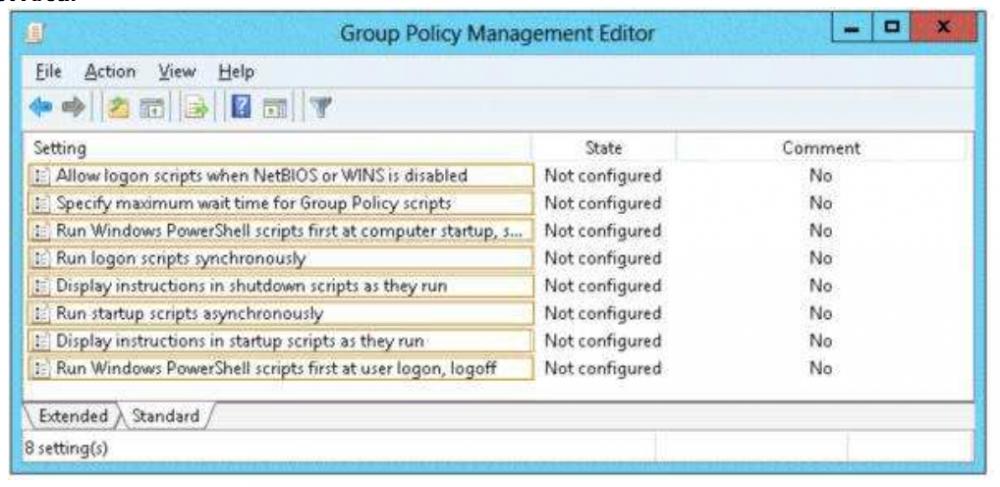
Run logon scripts synchronously
113.
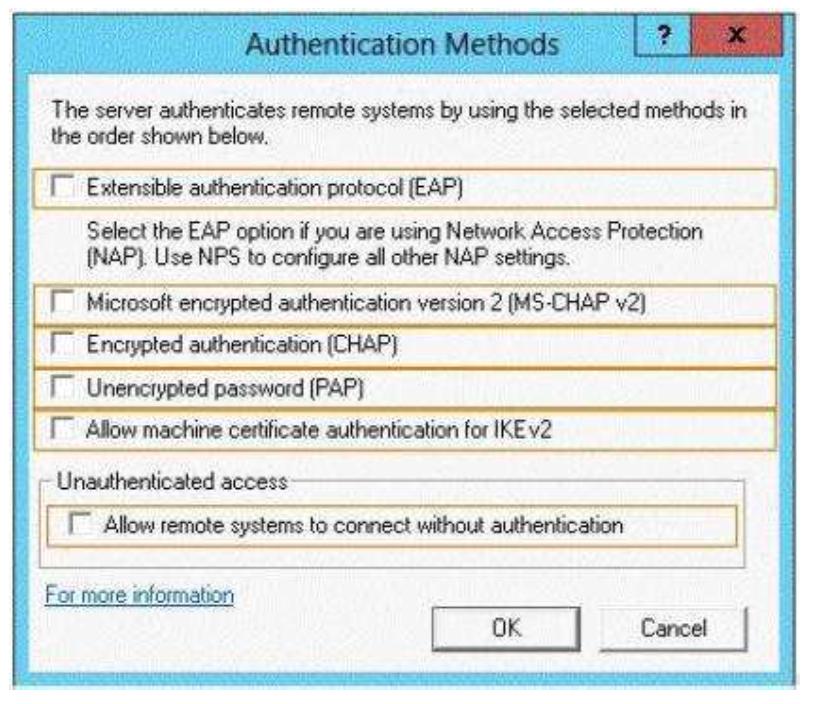
Extensible authentication protocot (EAP)
114.
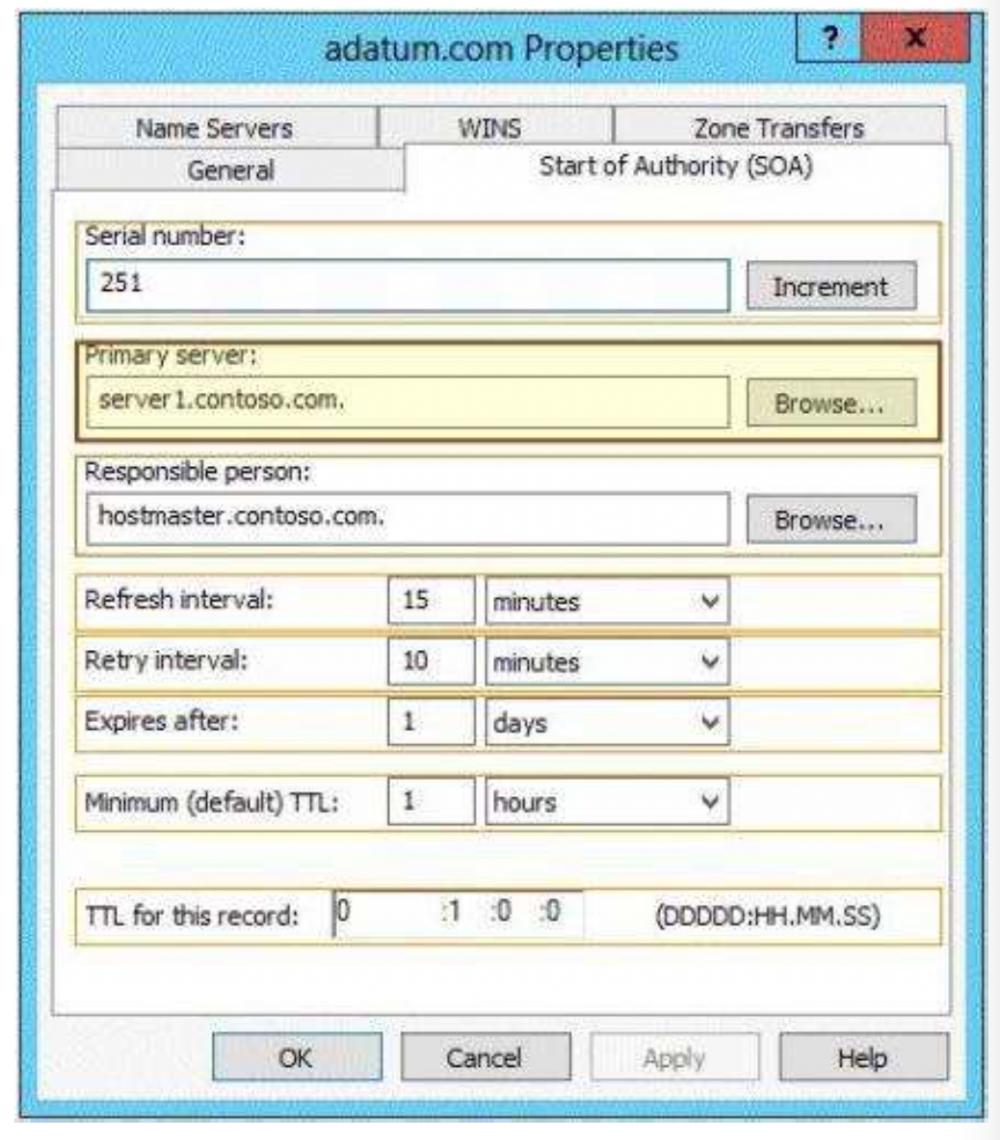
Serial number
115.
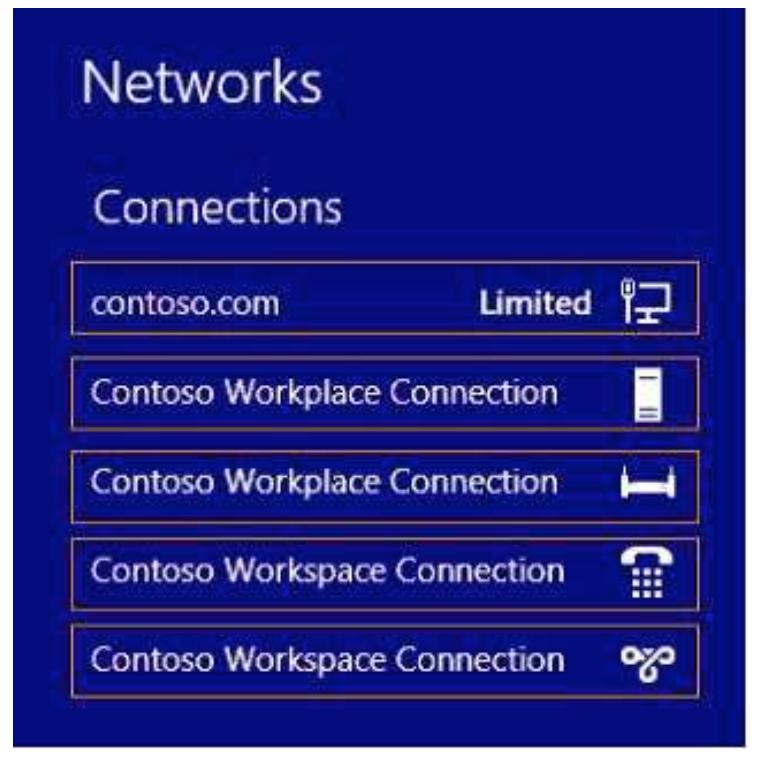
2
116.
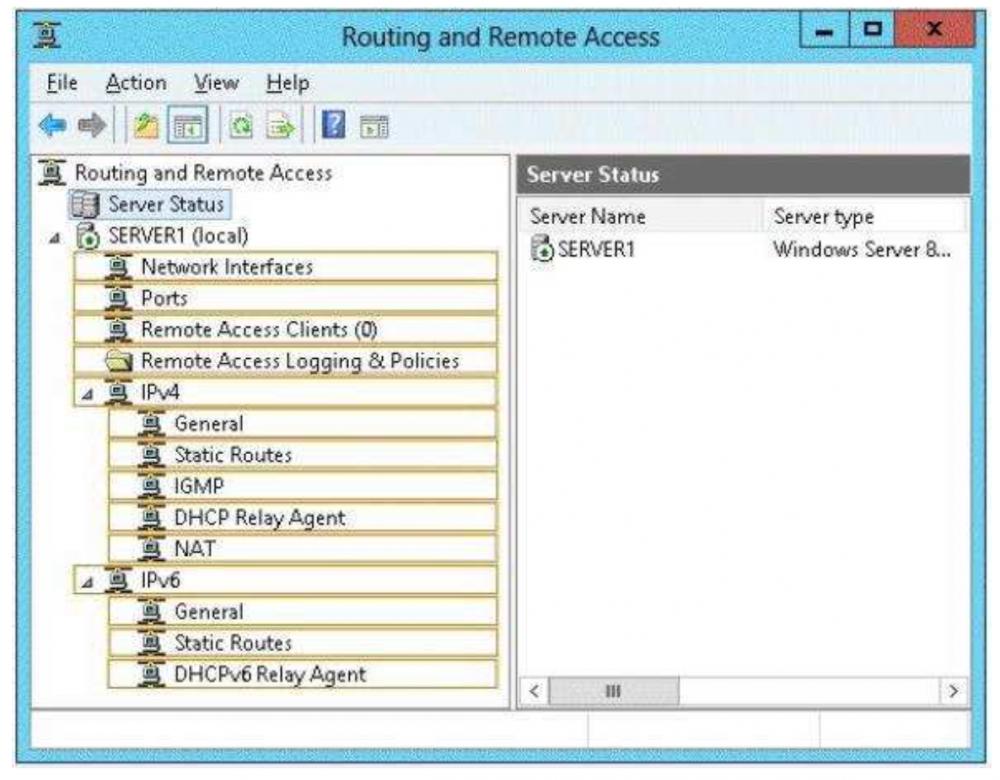
IPv4/General
117.
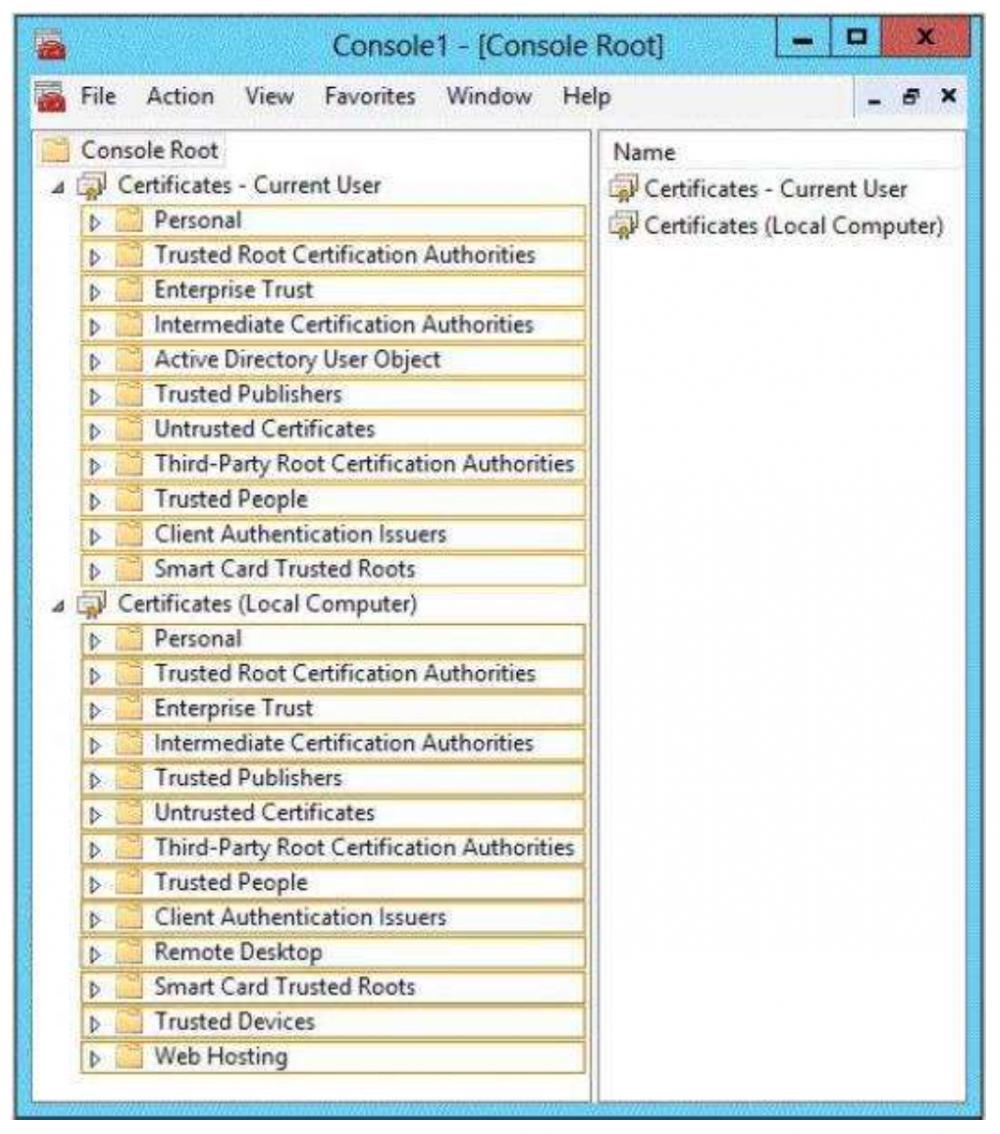
Certificates (local Computer) \ Personal
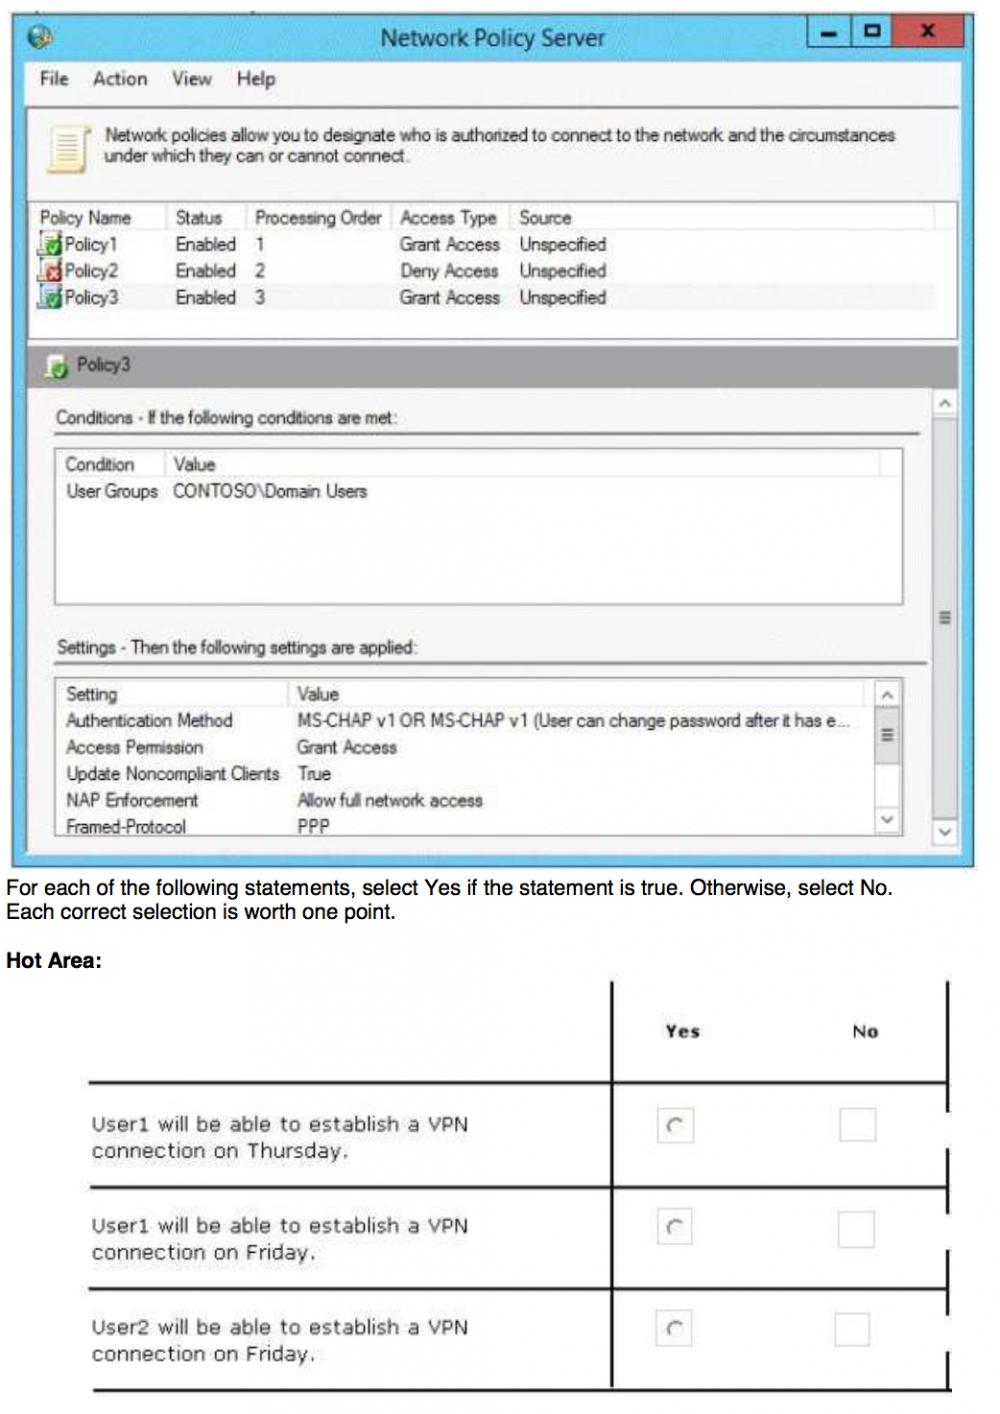
Your network contains an Active Directory named contoso.com.
You have users named User1 and user2.
The Network Access Permission for User1 is set to Control access through NPS Network Policy.
The Network Access Permission for User2 is set to Allow access.
A policy named Policyl is shown in the Policyl exhibit. (Click the Exhibit button.
Wpisz yes/no
118.
User1 will be able to establish a vpn connection on Thursday
yes
119.
User1 will be able to establish a vpn connection on Friday
no
120.
User2 will be able to establish a VPN connection on Friday
yes
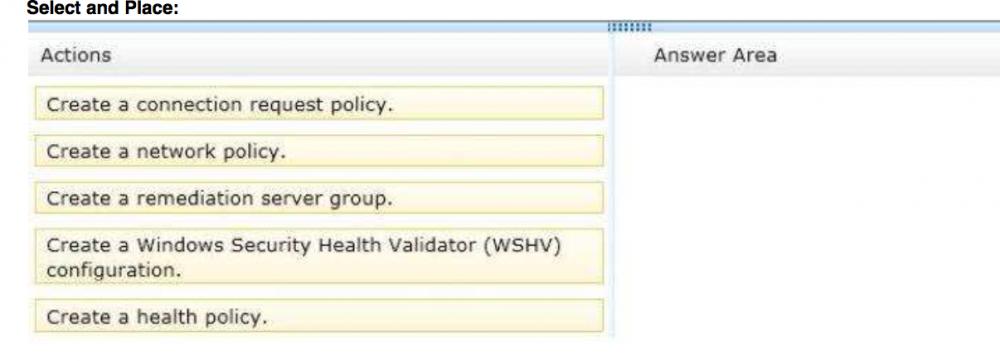
Your network contains an Active Directory domain named adatum.com. The domain contains a server named Server1 that runs Windows Server 2012 R2.
Server1 is configured as a Network Policy Server (NPS) server and as a DHCP server.
You need to log all DHCP clients that have Windows Firewall disabled.
Which three actions should you perform in sequence?
To answer, move the three appropriate actions from the list ot actions to the answer area and arrange them in the correct order.
Wpisz od 1-5
121.
1
4
122.
2
5
123.
3
2
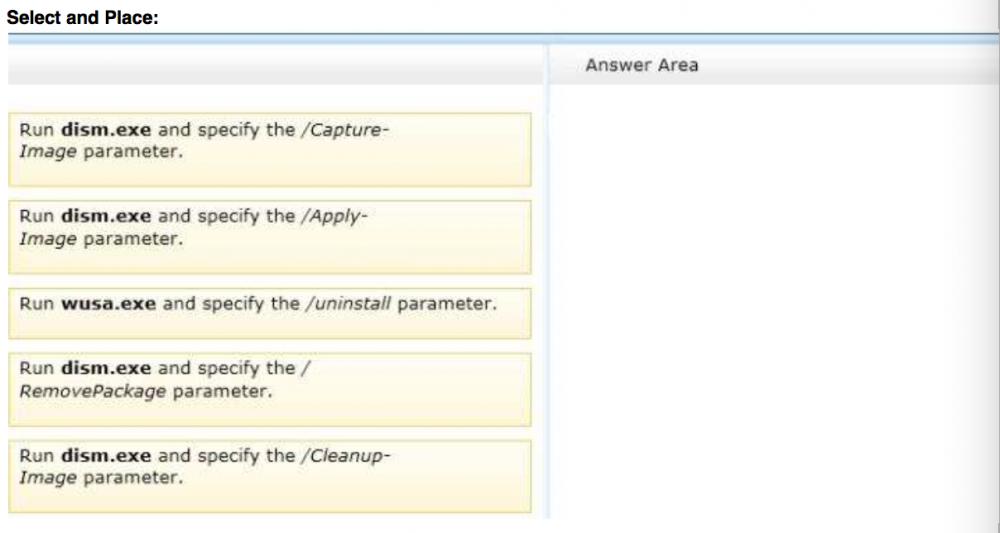
You have a WIM file that contains an image of Windows Server 2012 R2.
Recently, a technician applied a Microsoft Standalone Update Package (MSU) to the image.
You need to remove the MSU package from the image.
Which three actions should you perform in sequence?
To answer, move the appropriate three actions from the list of actions to the answer area and arrange them in the correct order.
Wpisz od 1 do 5 (cyfry)
124.
1
3
125.
2
4
126.
3
5
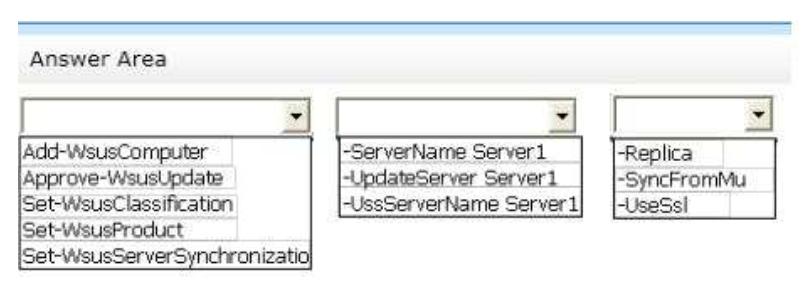
Your company has two offices. The offices are located in Montreal and Seattle.
The network contains an Active Directory domain named contoso.com. The domain contains servers named Server1 and Server2. Server1 is located in the Seattle office.
Server2 is located in the Montreal office.
Both servers run Windows Server 2012 R2 and have the Windows Server Update Services (WSUS) server role installed.
You need to configure Server2 to download updates that are approved on Server1 only.
What cmdlet should you run?
To answer, select the appropriate options in the answer area.
Wpisz 1-5
127.
1
5
128.
2
3
129.
3
1
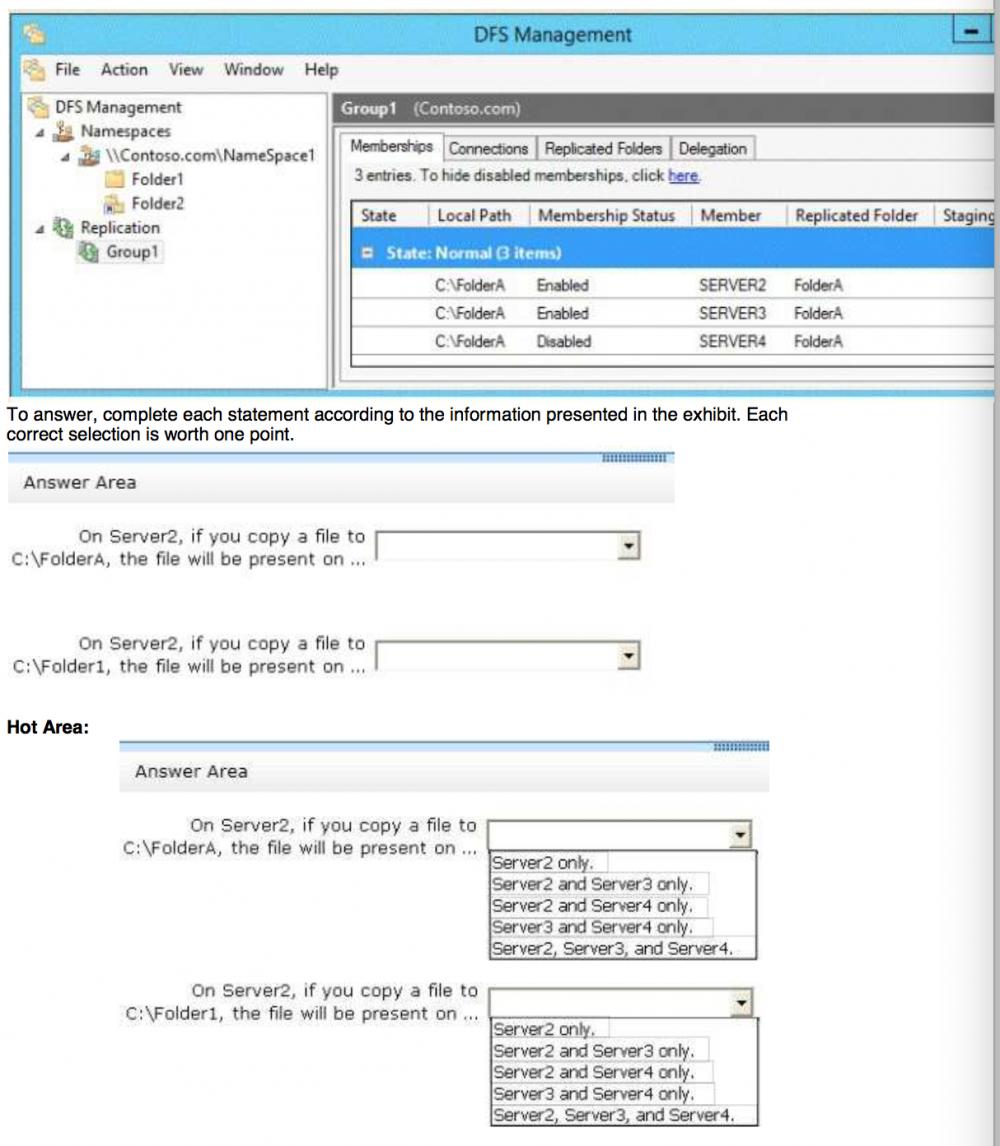
Your network contains an Active Directory domain named contoso.com. The domain contains three servers named Server2, Server3, and Server4.
Server2 and Server4 host a Distributed File System (DFS) namespace named Namespace1.
You open the DFS Management console as shown in the exhibit. (Click the Exhibit button.)
130.
1
Server2 and Server3 only
131.
2
Server2 only
132.
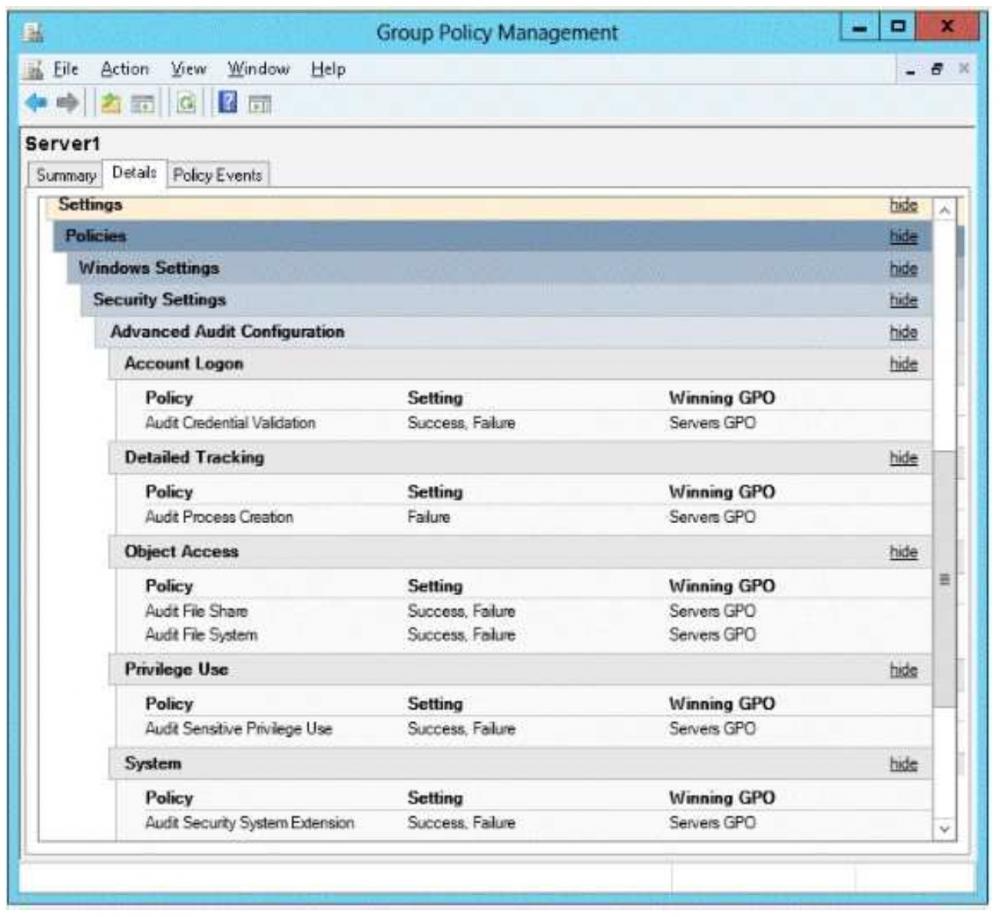
Object Access, Global Object Access Auditing
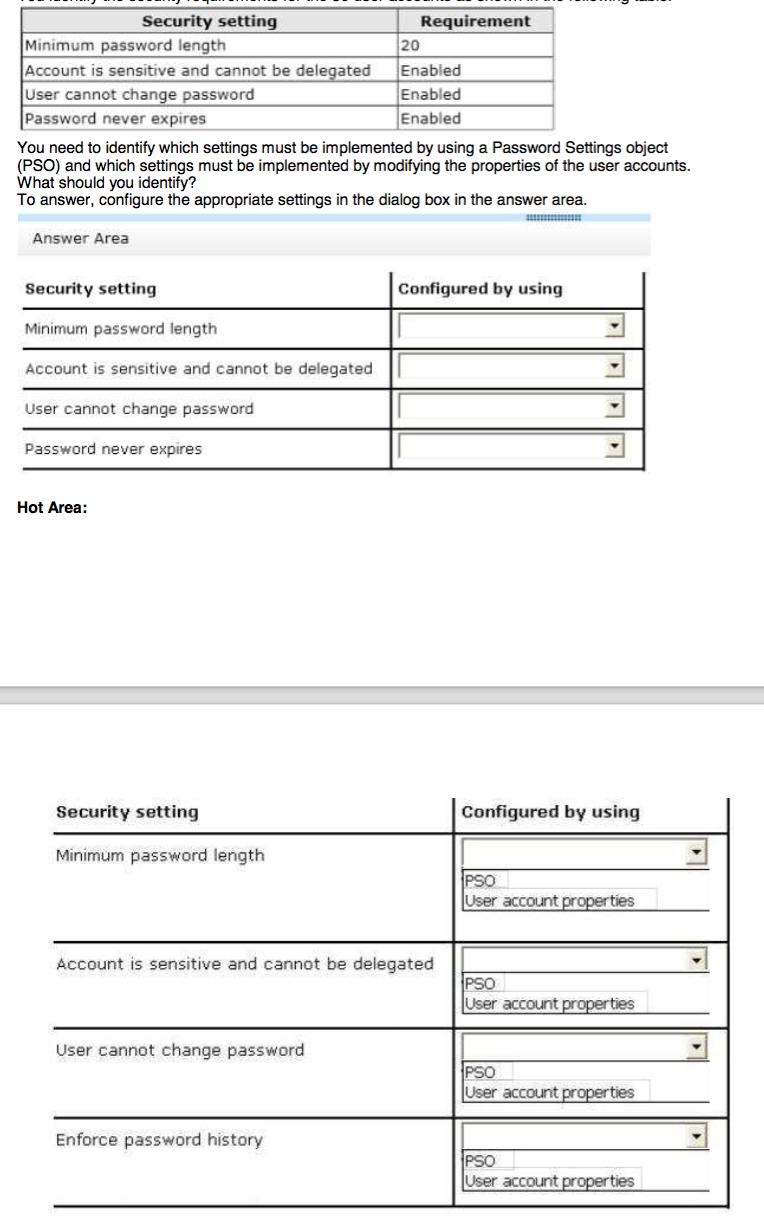
Your network contains an Active Directory domain named contoso.com. The domain contains 30 user accounts that are used for network administration. The user accounts are members of a domain global group named Group1.
You identify the security requirements for the 30 user accounts as shown in the following table.
You need to identify which settings must be implemented by using a Password Settings object (PSO) and which settings must be implemented by modifying the properties of the user accounts.
What should you identify?
To answer, configure the appropriate settings in the dialog box in the answer area.
Wpisz 1-2
133.
Minimum password length
1
134.
Account is sensitiue and cannot be delegated
2
135.
User cannot change passwor
2
136.
Enforce password history
1
137.
Detailed Tracking, Object Access
138.
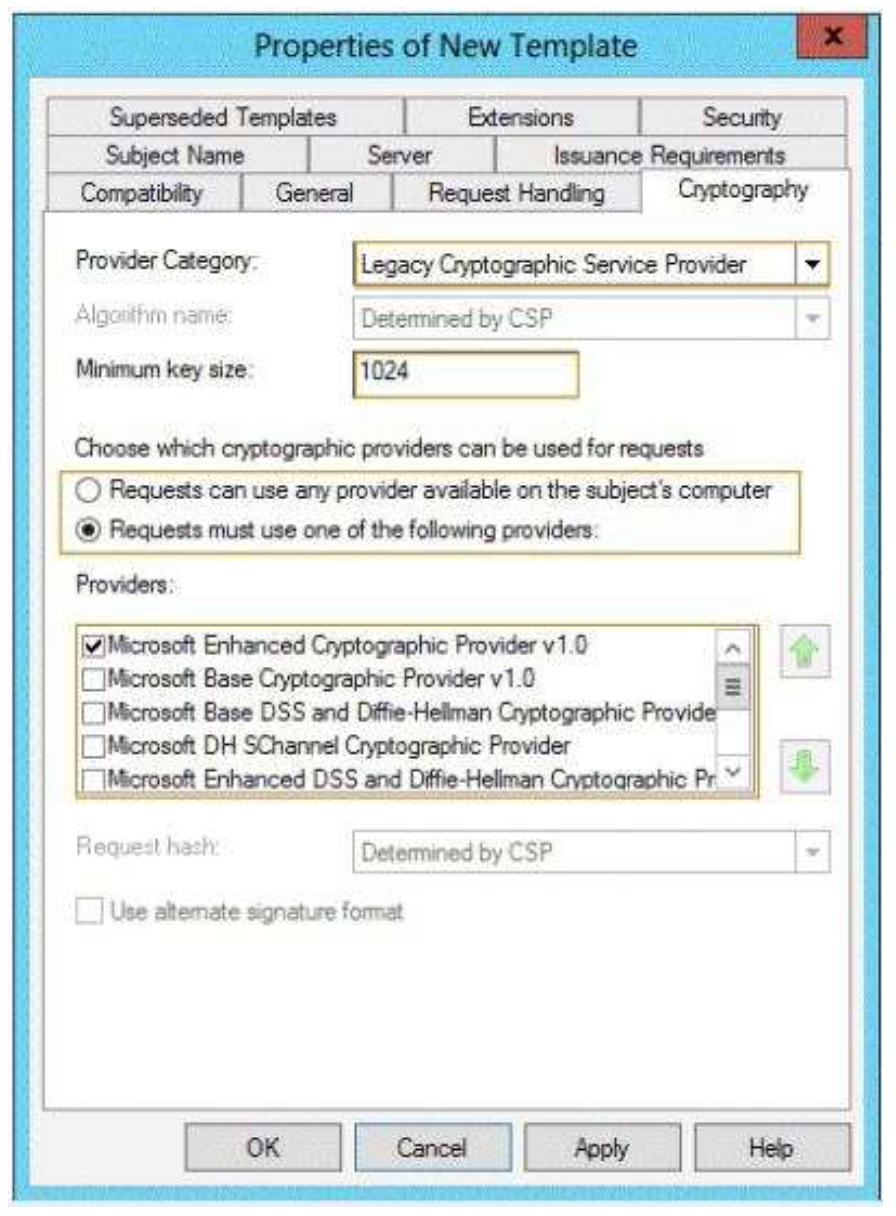
Minimum key size
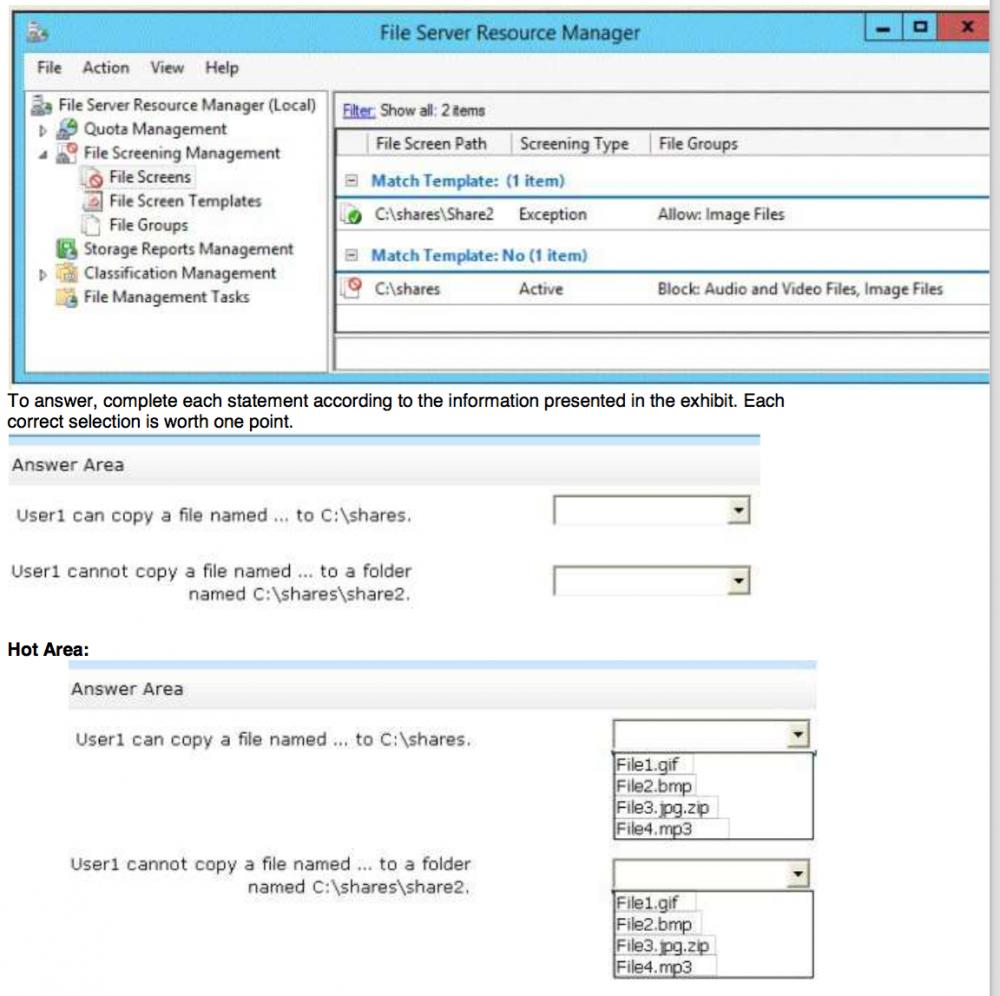
You have a file server named Server1 that runs Windows Server 2012 R2.
A user named Userl is assigned the modify NTFS permission to a folder named C:\shares and all of the subfolders of C:\shares.
On Server1, you open File Server Resource Manager as shown in the exhibit. (Click the Exhibit button.)
Wpisz od 1-4
139.
1
3
140.
2
4
141.
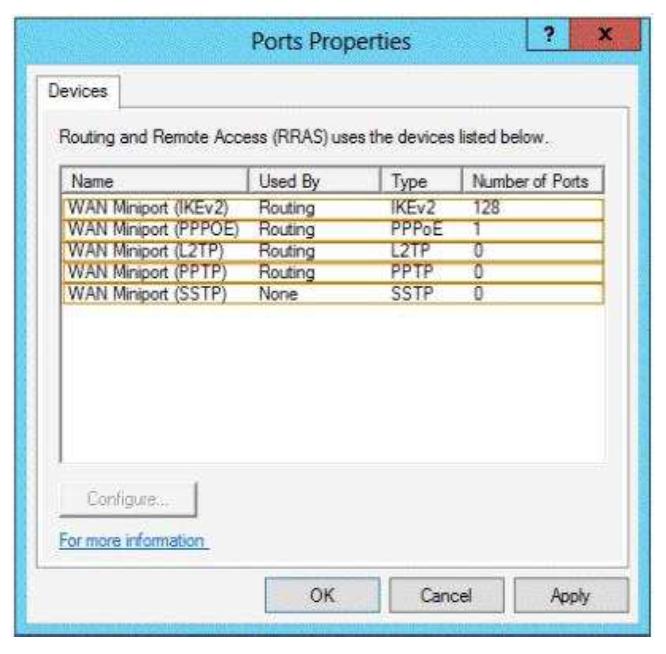
PPTP
142.
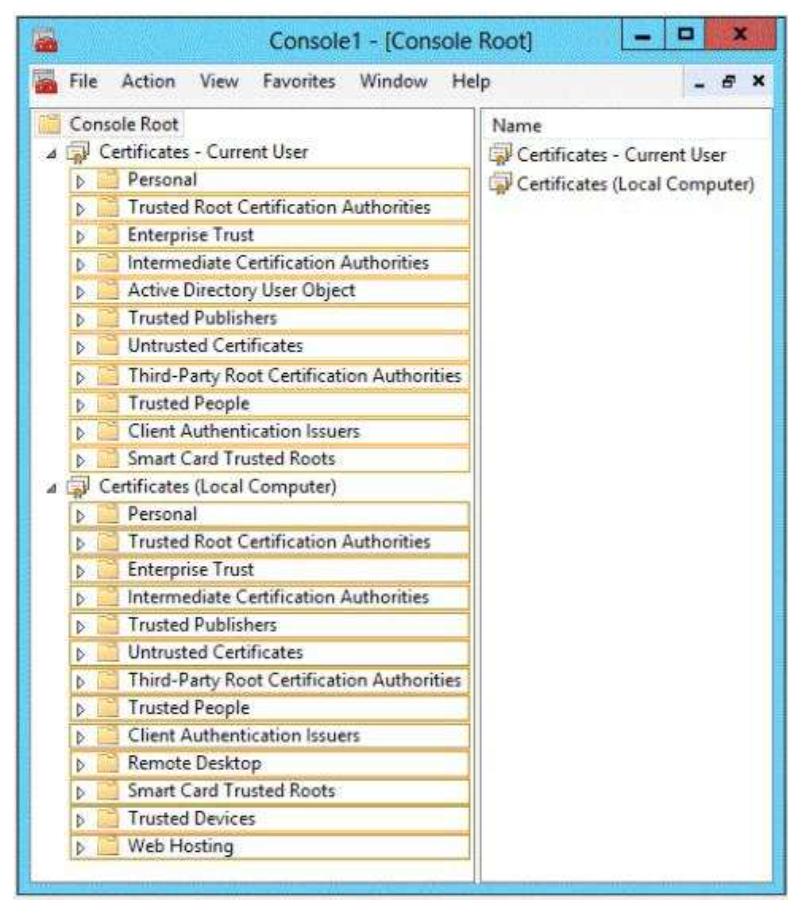
Certificates (Local Computer) / Personal
143.
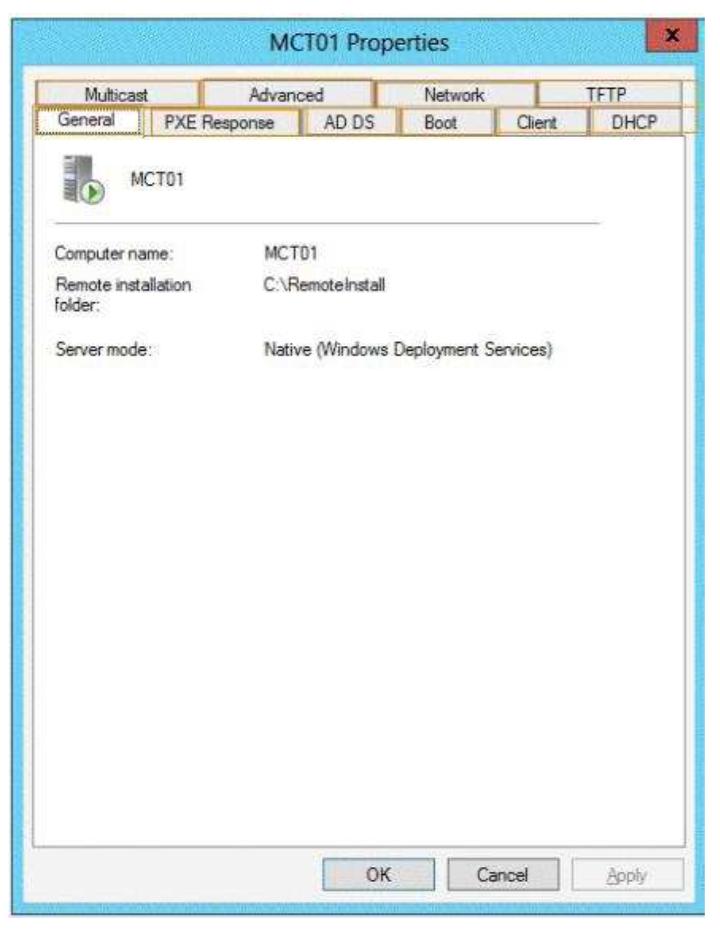
PXE Response
144.
Your network contains an Active Directory domain named contoso.com. All servers run Windows Server 2012 R2.
The domain contains a server named Server1 that has the Network Policy Server server role and the Remote Access server role installed. The domain contains a server named Server2 that is configured as a RADIUS server.
Server1 provides VPN access to external users.
You need to ensure that all of the VPN connections to Server1 are logged to the RADIUS server on Server2.
What should you run?
Add-RemoteAccessRadius -ServerName Server2 -AccountingOnOffMsg Enabled -SharedSecret "Secret" -Purpose Accounting
145.
Your network contains an Active Directory domain named contoso.com.
All domain controllers run Windows Server 2012 R2.
On all of the domain controllers, Windows is installed in C:\Windows and the Active Directory database is located in D:\Windows\NTDS\.
All of the domain controllers have a third-party application installed. The operating system fails to recognize that the application is compatible with domain controller cloning.
You verify with the application vendor that the application supports domain controller cloning.
You need to prepare a domain controller for cloning.
What should you do?
In D:\Windows\NTDS\, create an XML file named CustomDCCIoneAllowList.xml and add the application information to the file
146.
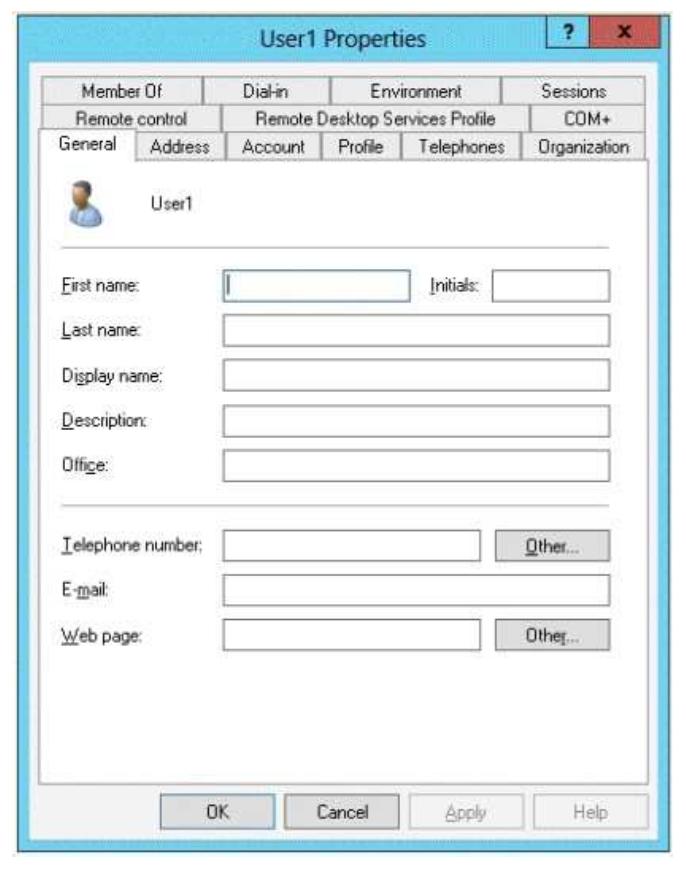
Configure a Service Principal Name (SPN) for User1
147.
Your network contains an Active Directory forest named contoso.com. The forest functional level is Windows Server 2012 R2. The forest contains a single domain. You create a Password Settings object (PSO) named PS01.
You need to delegate the rights to apply PS01 to the Active Directory objects in an organizational unit named 0U1.
What should you do?
From Active Directory Administrative Center, modify the security settings of PS01
148.
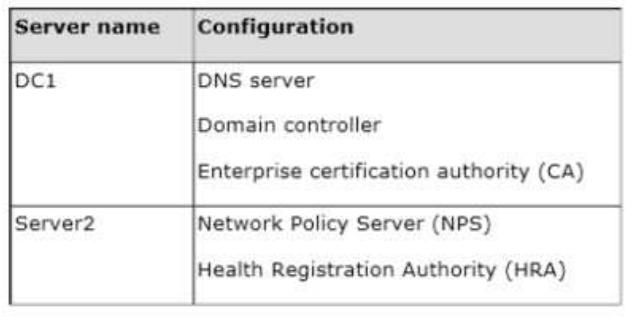
On all ot the client computers, configure the EnableDiscovery registry key, In a GPO, modify the Request Policy setting for the NAP Client Configuration, On DC1, create a service location (SRV) record
149.
Your network contains two Active Directory forests named contoso.com and adatum.com. The contoso.com
forest contains a server named Server1.contoso.com. The adatum.com forest contains a server named
server2. adatum.com. Both servers have the Network Policy Server role service installed.
The network contains a server named Server3. Server3 is located in the perimeter network and has the
Network Policy Server role service installed.
You plan to configure Server3 as an authentication provider for several VPN servers. You need to ensure
that RADIUS requests received by Server3 for a specific VPN server are always forwarded to
Server1 .contoso.com.
Which two should you configure on Server3? (Each correct answer presents part ot the solution.
Choose two.)
Remote RADIUS server groups, Connection request policies
150.
Your network contains an Active Directory domain named contoso.com. The domain contains a server named Server1 that runs Windows Server 2012 R2. Server1 has the Network Policy and Access Services server role installed.
Your company's security policy requires that certificate-based authentication must be used by some network services.
You need to identify which Network Policy Server (NPS) authentication methods comply with the security
policy.
Which two authentication methods should you identify? (Each correct answer presents part ot the soiution.
Choose two.)
PEAP-MS-CHAP v2, EAP-TLS
151.
Your network contains an Active Directory domain named adatum.com. The domain contains a file server named Server1 that runs Windows Server 2012 R2.
All client computers run Windows 7.
You need to ensure that user settings are saved to \\Server1\Users\.
What should you do?
From the properties of each user account, configure the User profile settings
152.
Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012 R2.
An organizational unit (OU) named OU1 contains 200 client computers that run Windows 8 Enterprise.
A Group Policy object (GPO) named GP01 is linked to OU1.
You make a change to GP01.
You need to force all of the computers in OU1 to refresh their Group Policy settings immediately.
The solution must minimize administrative effort.
Which tool should you use?
Group Policy Management Console (GPMC)
153.
Your network contains an Active Directory domain named contoso.com. The domain contains a domain controller named DC1 that runs Windows Server 2012 R2.
All client computers run Windows 8 Enterprise.
DC1 contains a Group Policy object (GPO) named GP01.
You need to update the PATH variable on all of the client computers.
Which Group Policy preference should you configure?
Environment
154.
Your company has a main office and a branch office.
The main office contains a server that hosts a Distributed File System (DFS) replicated folder. You plan to
implement a new DFS server in the branch office. You need to recommend a solution that minimizes the
amount of network bandwidth used to perform the initial synchronization of the folder to the branch office.
You recommend using the Export-DfsrClone and Import-DfsrCIonecmdlets. Which additional command or
cmdlet should you include in the recommendation?
Robocopy.exe
155.
Your network contains an Active Directory domain named contoso.com. The domain contains two servers named Server1 and Server2.
Both servers run Windows Server 2012 R2.
Both servers have the File and Storage Services server role, the DFS Namespaces role service, and the DFS Replication role service installed.
Server1 and Server2 are part of a Distributed File System (DFS) Replication group named Group1.
Server1 and Server2 are separated by a low-speed WAN connection. You need to limit the amount of bandwidth
that DFS can use to replicate between Server1 and Server2.
What should you modify?
The schedule of the replication group
156.
You have a file server named Server1 that runs Windows Server 2012 R2.
Server1 has the File Server Resource Manager role service installed.
Files created by users in the human resources department are assigned the Department classification property automatically.
You are configuring a file management task named Task1 to remove user files that have not bene accessed for 60 days or more.
You need to ensure that Task1 only removes files that have a Department classification property of human resources.
The solution must minimize administrative effort.
What should you configure on Task1 ?
Create a condition
157.
Your network contains an Active Directory domain named contoso.com. All domain controllers run Windows Server 2012 R2. You plan to use fine-grained password policies to customize the password policy settings of contoso.com.
You need to identify to which Active Directory object types you can directly apply the finegrained password policies.
Which two object types should you identify? (Each correct answer presents part ot the solution.
Choose two.)
Users, Global groups
158.
You have a cluster named Cluster1 that contains two nodes. Both nodes run Windows Server 2012 R2.
Cluster1 hosts a virtual machine named VM1 that runs Windows Server 2012 R2.
You configure a custom service on VM1 named Service1.
You need to ensure that VM1 will be moved to a different node if Service1 fails.
Which cmdlet should you run on Cluster1?
Add-ClusterVmMonitoredltem
159.
You have a server named Server1 that runs Windows Server 2012 R2. Server1 has the Windows Server Update Services server role installed.
You need to configure Windows Server Update Services (WSUS) to support Secure Sockets Layer (SSL).
Which three actions should you perform?
(Each correct answer presents part ot the solution. Choose three.)
Install a server certificate, Run the wsusutil.exe command, From Internet Information Services (IIS) Manager, modify the bindings ot the WSUS website
160.
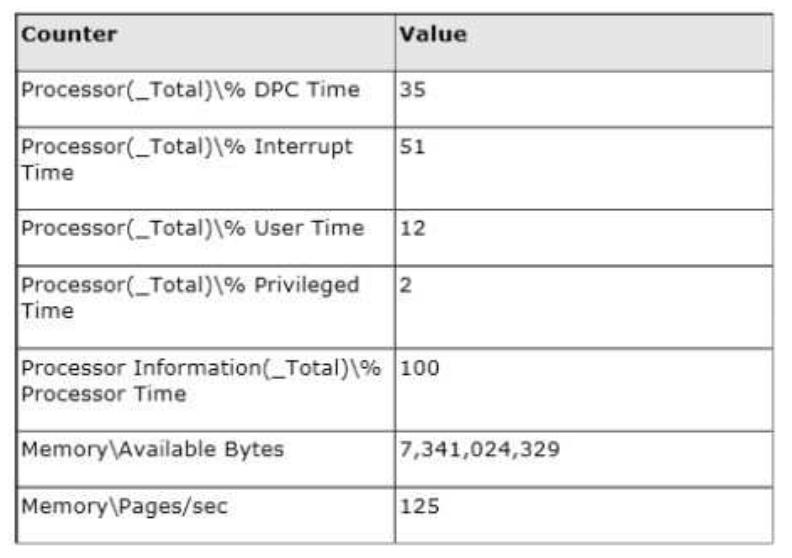
Driver malfunction
161.
Your network contains an Active Directory domain named contoso.com. The domain contains two member servers named Server1 and Server2.
All servers run Windows Server 2012 R2.
Server1 and Server2 are nodes in a Hyper-V cluster named Cluster1. Cluster1 hosts 10 virtual machines.
All of the virtual machines run Windows Server 2012 R2 and are members of the domain.
You need to ensure that the first time a service named Service1 fails on a virtual machine, the virtual machine is moved to a different node.
You configure Service1 to be monitored from Failover Cluster Manager.
What should you configure on fhe virtual machine?
From the Recovery settings of Service1, set the First failure recovery action to Take No Action
162.
You have a DNS server named Server1 that runs Windows Server 2012 R2.
On Server1, you create a DNS zone named contoso.com.
You need to specify the email address of the person responsible for the zone.
Which type of DNS record should you configure?
Start of authority (SOA)
163.
Your network contains an Active Directory forest.
The forest contains two domains named contoso.com and
fabrikam.com.
All of the DNS servers in both of the domains run Windows Server 2012 R2.
The network contains two servers named Server1 and Server2.
Server1 hosts an Active Directory-integrated zone for contoso.com. Server2 hosts an Active Directory-integrated zone for fabrikam.com.
Server1 and Server2 connect to each other by using a WAN link. Client computers that connect to Server1
for name resolution cannot resolve names in fabrikam.com.
You need to configure Server1 to resolve names in fabrikam.com. The solution must NOT require that
changes be made to the fabrikam.com zone on Server2.
What should you create?
A stub zone